The cybersecurity risk & resilience ecosystem
Modular products that work together. Start with a single assessment and evolve into continuous, managed security — across AI, cloud, identity, email, endpoints, compliance and resilience.
Every cybersecurity domain, one platform
Each CyberSecurer product is a focused assessment and action module. Use them individually or together.
CyberSecurer Assess
AI-assisted cybersecurity risk assessment
Understand your organization's cybersecurity posture and identify the risks requiring immediate attention.
- Security questionnaire
- Risk scoring
- Gap analysis
- Executive report
- Technical findings
- Remediation roadmap
CyberSecurer AI Shield
AI security & AI governance assessment
Assess AI applications, AI agents, LLM usage, shadow AI, sensitive-data exposure, prompt-injection risk, AI permissions, non-human identities and AI vendor risk — including OSINT-informed attacks where adversaries use publicly available information to craft targeted prompts and social-engineer AI agents.
- AI application inventory
- Shadow AI detection
- Prompt-injection risk
- OSINT-informed AI attacks
- AI governance
- Non-human identities
CyberSecurer OSINT
External attack-surface & OSINT exposure assessment
Assess what an attacker can learn about your organization from open sources before they ever touch your network. CyberSecurer OSINT reviews public records, leaked credentials, code repositories, exposed cloud assets, DNS, certificates, social media and executive exposure — the same intelligence a real-world adversary gathers to plan phishing, BEC and targeted attacks.
- External attack-surface mapping
- Leaked credential monitoring
- Code & repository exposure
- DNS & certificate exposure
- Executive & social exposure
- Attacker-perspective reporting
CyberSecurer Cloud
Cloud security assessment for AWS, Azure & GCP
Assess IAM, MFA, privileged access, storage exposure, encryption, logging, backups, network configuration, cloud workloads and APIs.
- AWS, Azure & GCP
- IAM & privileged access
- Storage exposure
- Encryption & logging
- Backup posture
- Workloads & APIs
CyberSecurer Identity
Identity and access security
Assess user accounts, privileged accounts, MFA, dormant accounts, excessive privileges, service accounts, machine identities and AI-agent identities.
- MFA coverage
- Privileged accounts
- Dormant accounts
- Service accounts
- Machine identities
- AI-agent identities
CyberSecurer Email
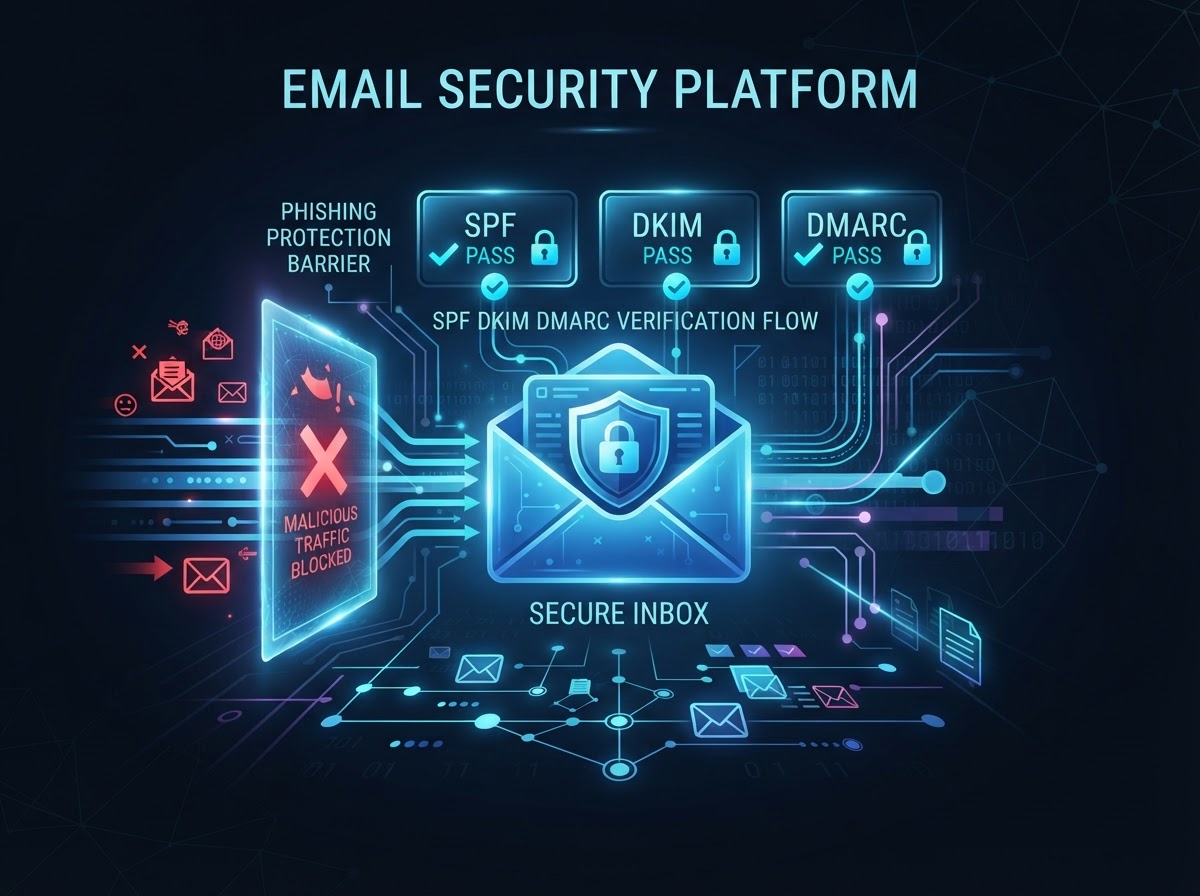
Email & business-email security
Phishing risk assessment, SPF/DKIM/DMARC assessment, business email compromise awareness, phishing simulation and employee awareness.
- Phishing risk
- SPF / DKIM / DMARC
- BEC awareness
- Phishing simulation
- Employee awareness
- Email hardening
CyberSecurer Vulnerability
Authorized vulnerability & exposure management
External attack-surface assessment, vulnerability identification, configuration assessment, prioritized findings and remediation recommendations.
- External attack surface
- Vulnerability ID
- Configuration assessment
- Prioritized findings
- Remediation guidance
CyberSecurer Compliance
Cybersecurity compliance & control assessment
Assess readiness against NIST CSF, NIST SP 800-53, CIS Controls, ISO/IEC 27001, SOC 2, PCI DSS, HIPAA, GDPR and PIPEDA. CyberSecurer helps organizations assess readiness and identify control gaps.
- NIST CSF & 800-53
- CIS Controls
- ISO 27001 & SOC 2
- PCI DSS
- HIPAA / GDPR / PIPEDA
- Control-gap mapping
CyberSecurer Resilience
Cyber resilience & ransomware readiness
Assess backup strategy, recovery, incident response, privileged access, MFA, segmentation, endpoint protection, business continuity and disaster recovery.
- Backup & recovery
- Incident response
- Segmentation
- Endpoint protection
- Business continuity
- Disaster recovery
CyberSecurer Academy
Security awareness & employee training
Training across phishing, ransomware, passwords, MFA, social engineering, AI security, data protection, remote work, mobile security and business email compromise.
- Phishing & ransomware
- Passwords & MFA
- Social engineering
- AI security
- Remote & mobile
- BEC training
CyberSecurer 24/7
Managed cybersecurity services
Continuous monitoring, vulnerability monitoring, security alerts, posture reports, incident escalation, security advisory and managed security integrations. Actual 24/7 monitoring is provided only where the appropriate monitoring/SOC infrastructure is connected.
- Continuous monitoring
- Vulnerability monitoring
- Security alerts
- Posture reports
- Incident escalation
- Managed integrations
Your external exposure, mapped
Before an attacker touches your network, they gather open-source intelligence (OSINT) — public records, leaked credentials, exposed cloud assets, code repositories, DNS, certificates and staff details. CyberSecurer OSINT reviews the same surface a real-world adversary would, so you can close it.
Exposed assets
14
Leaked credentials
3
Public code repos
7
Executive exposure
2
Demonstration data — not a real OSINT assessment.
See what an attacker already knows about you
Modern attackers use open-source intelligence to plan phishing, business email compromise and targeted AI attacks — crafting prompts and social-engineering staff using details scraped from public sources. CyberSecurer OSINT maps that exposure from an attacker's perspective and turns it into prioritized remediation.
- External attack-surface & exposed-asset discovery
- Leaked credential and data-breach monitoring
- Code repository, DNS and certificate exposure
- OSINT-informed AI and social-engineering risk
Outsourced cybersecurity for SMBs
For organizations without a dedicated security team — a packaged, affordable continuous program.
What's included
- Security assessment
- Vulnerability monitoring
- Domain monitoring
- Email security review
- Identity review
- AI security review
- Monthly report
- Security awareness
- Security advisory
Designed for organizations that do not have a dedicated security team. CyberSecurer becomes your outsourced cybersecurity partner.